CVE-2024-26152
CVE-2024-26152 · Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Diese Seite enthält Fakten aus öffentlichen Sicherheitsquellen. Lesen Sie vor dem Aktualisieren die Originalmeldung.
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 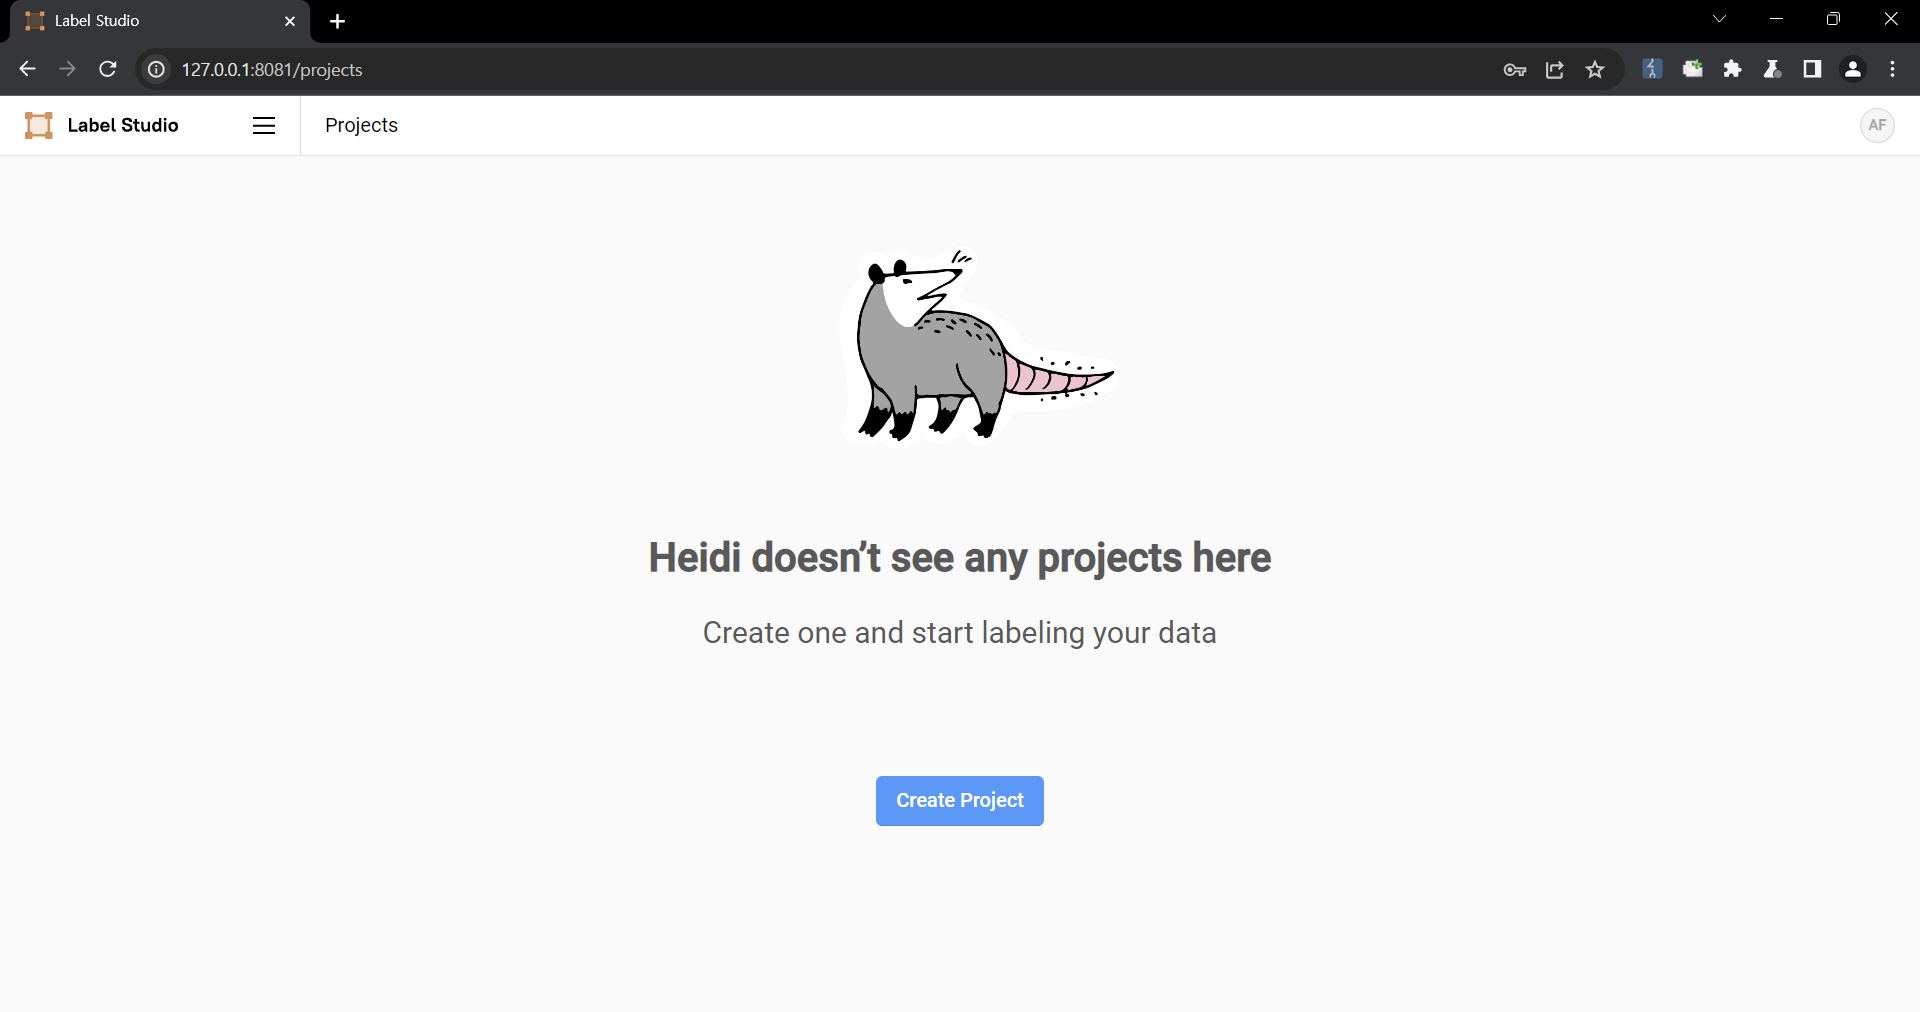 2. Upload a file containing the payload using the "Upload Files" function. 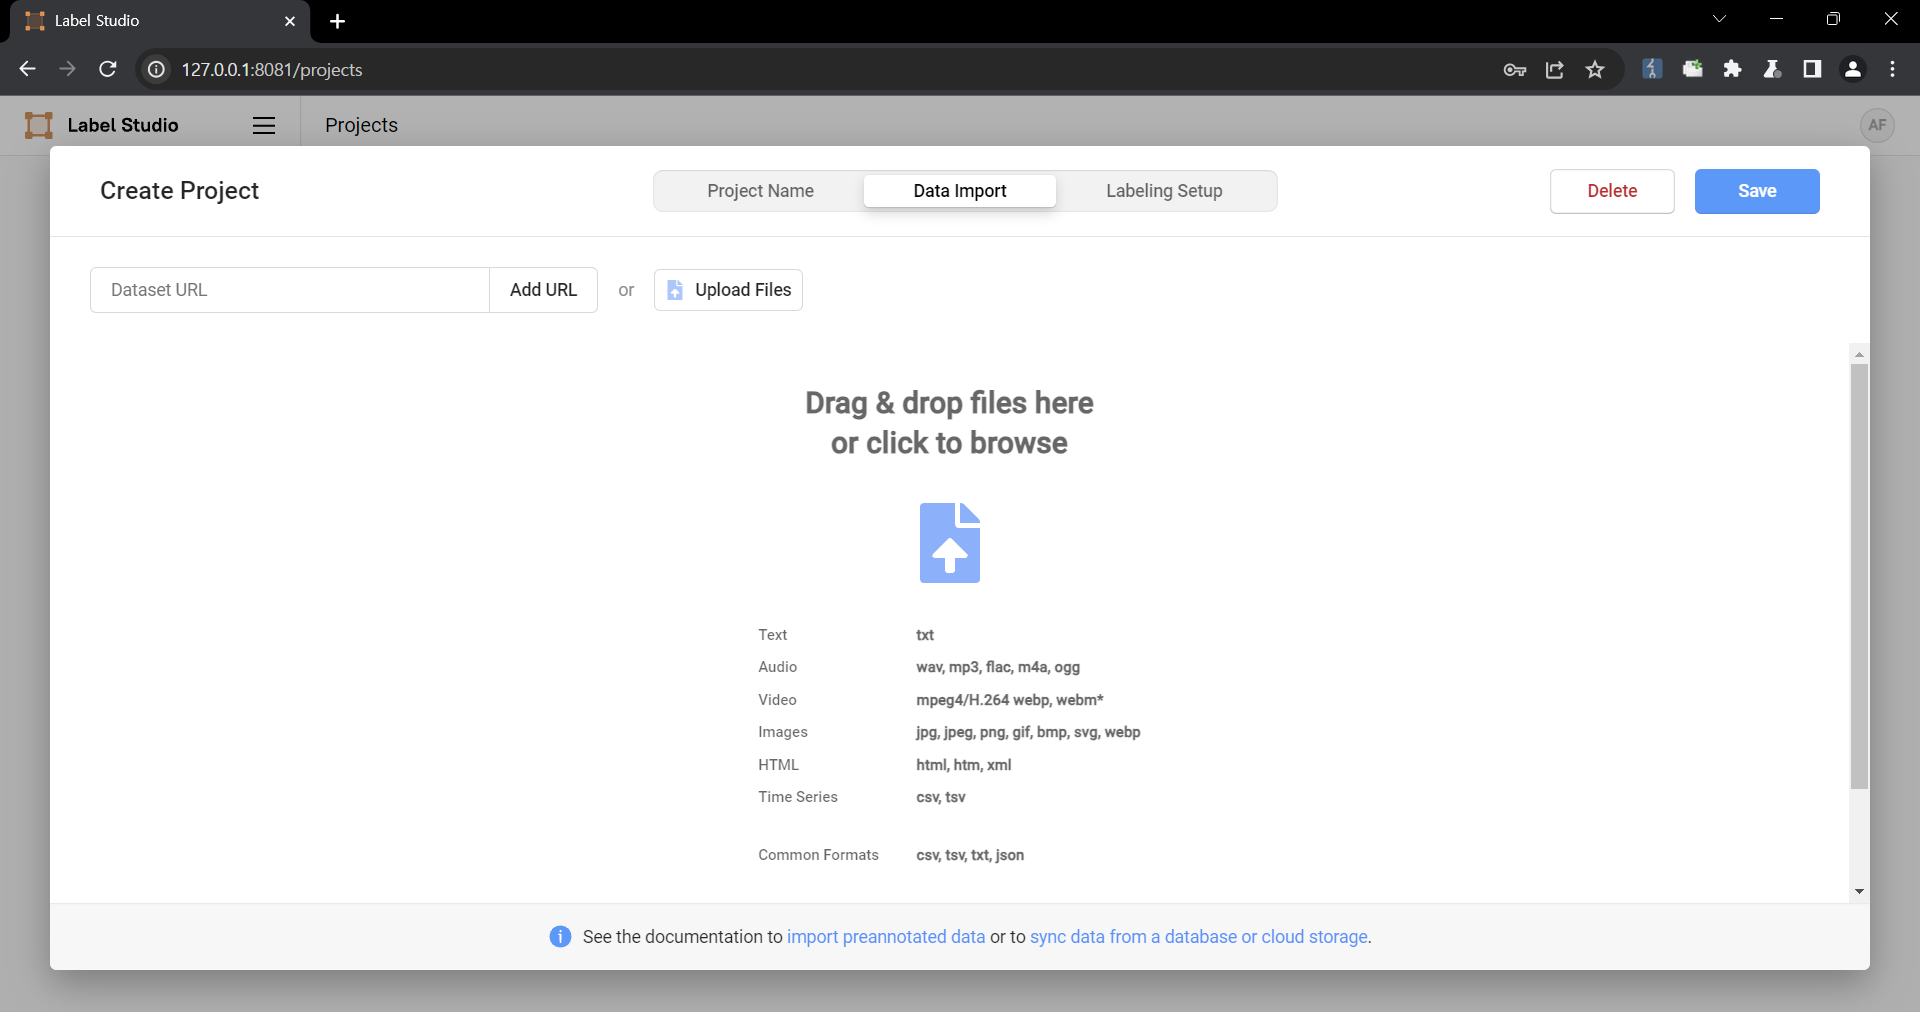 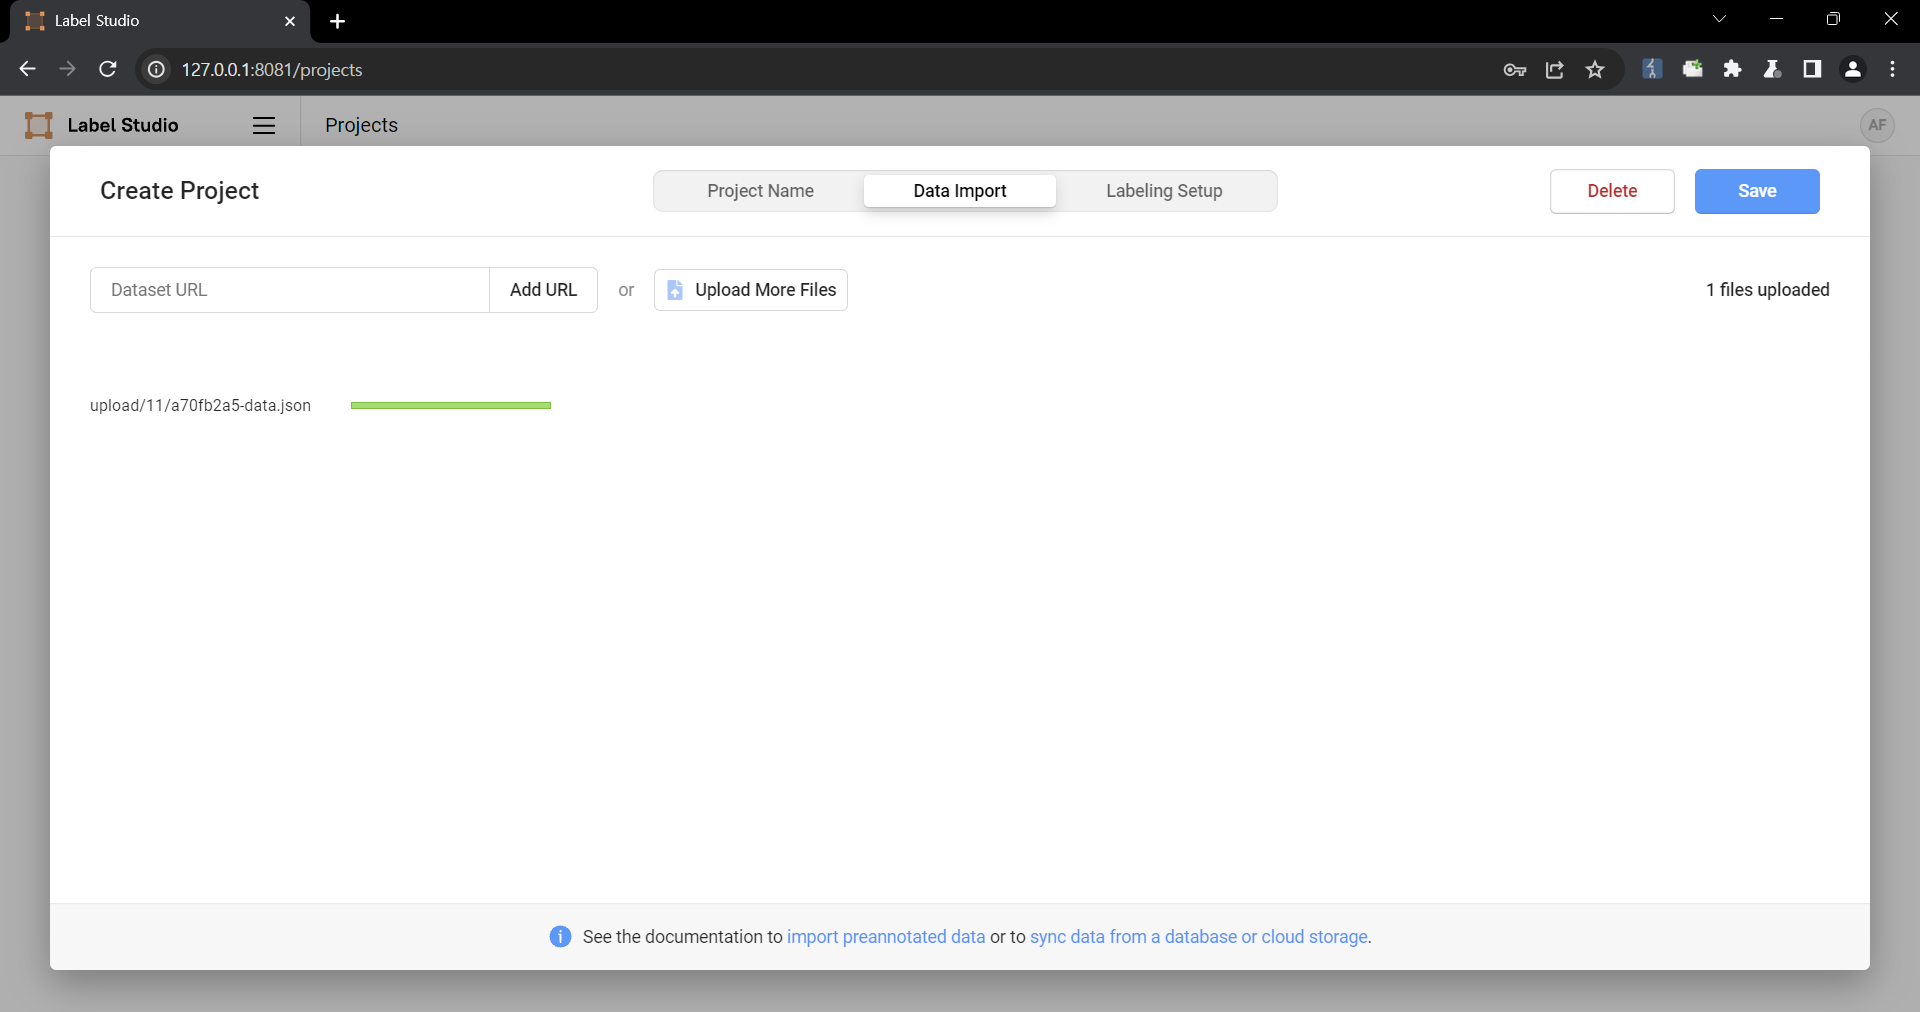 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 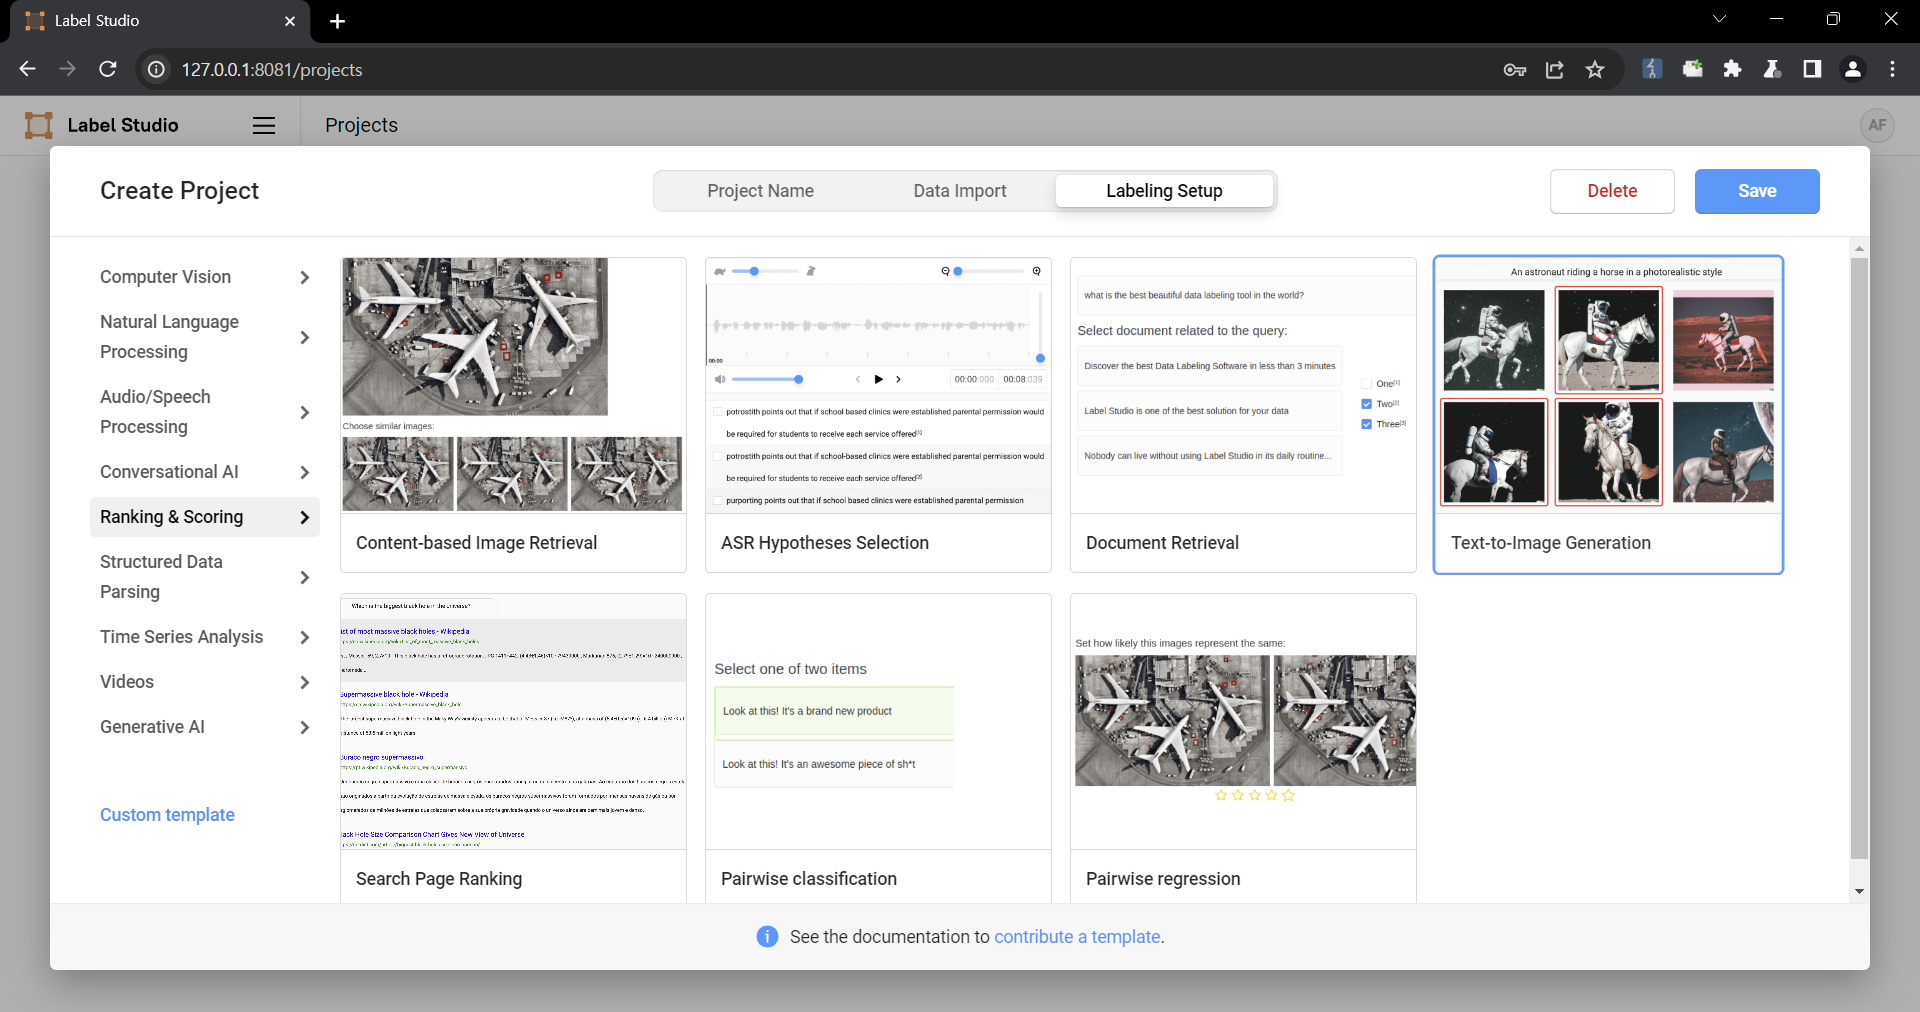 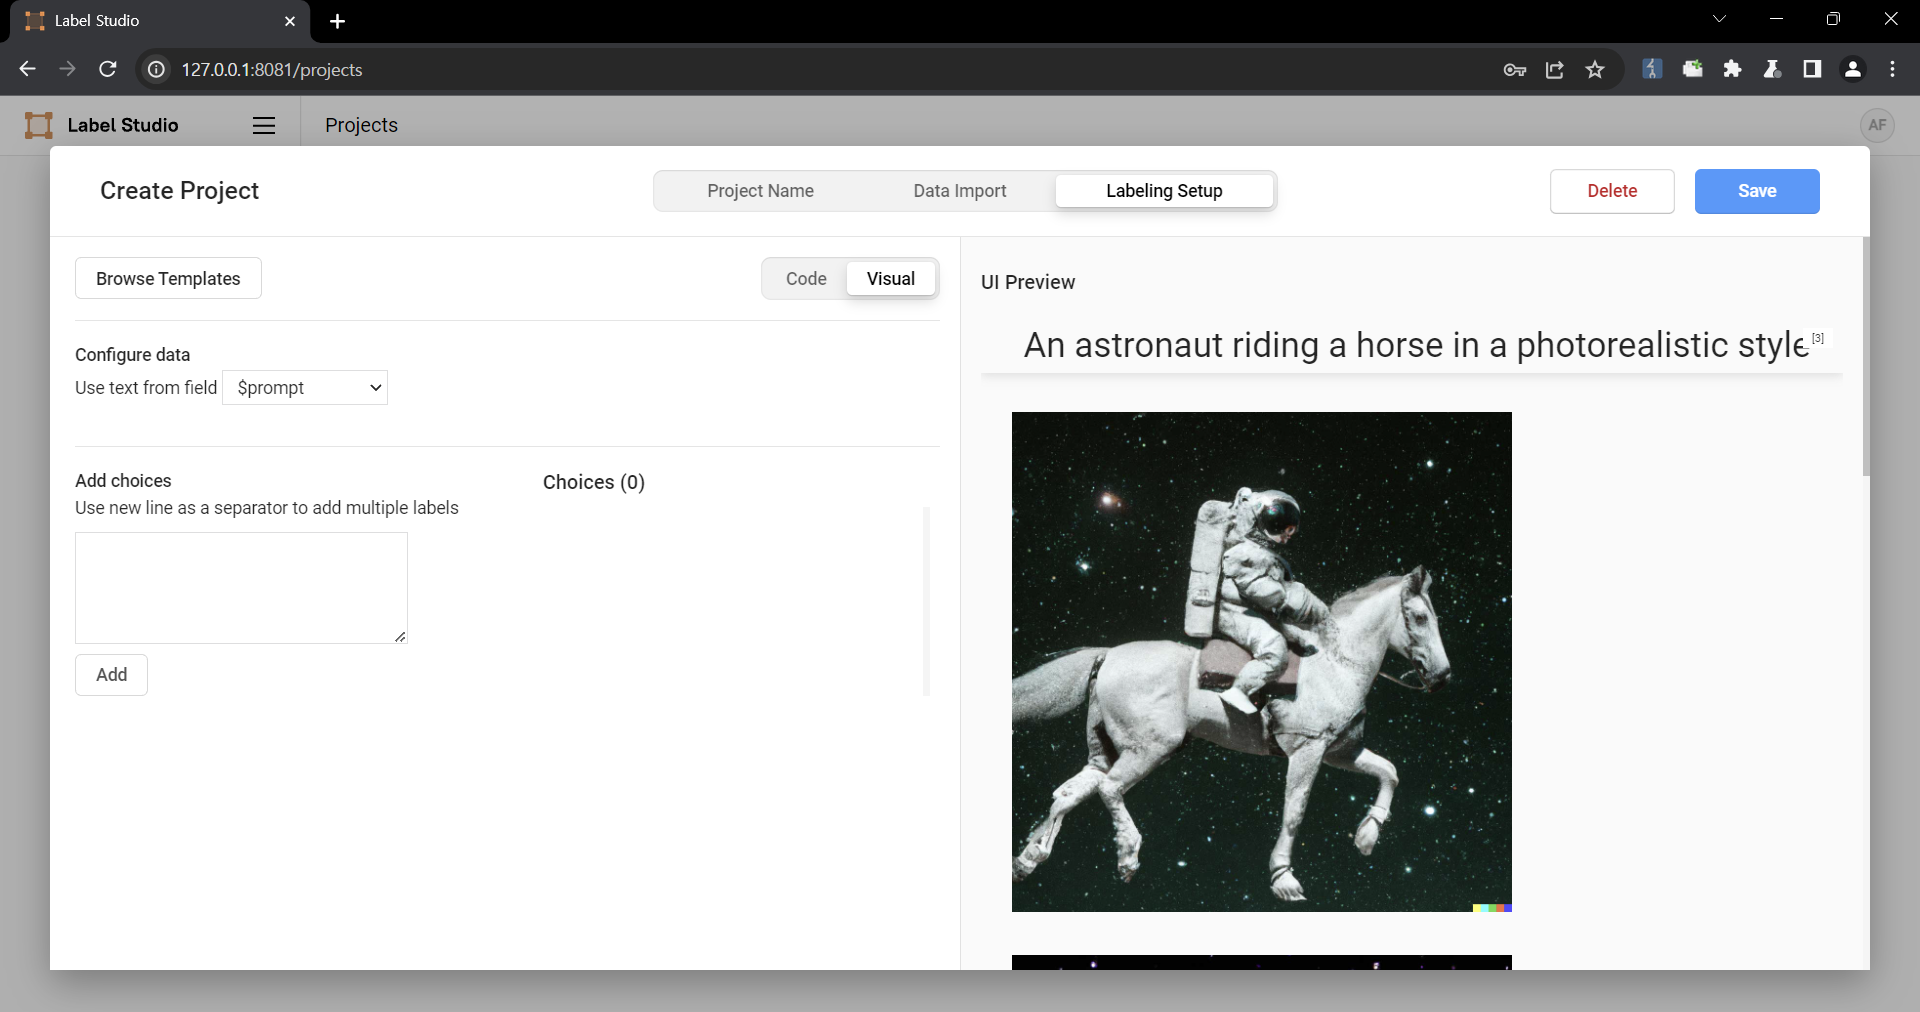 4. Select a task 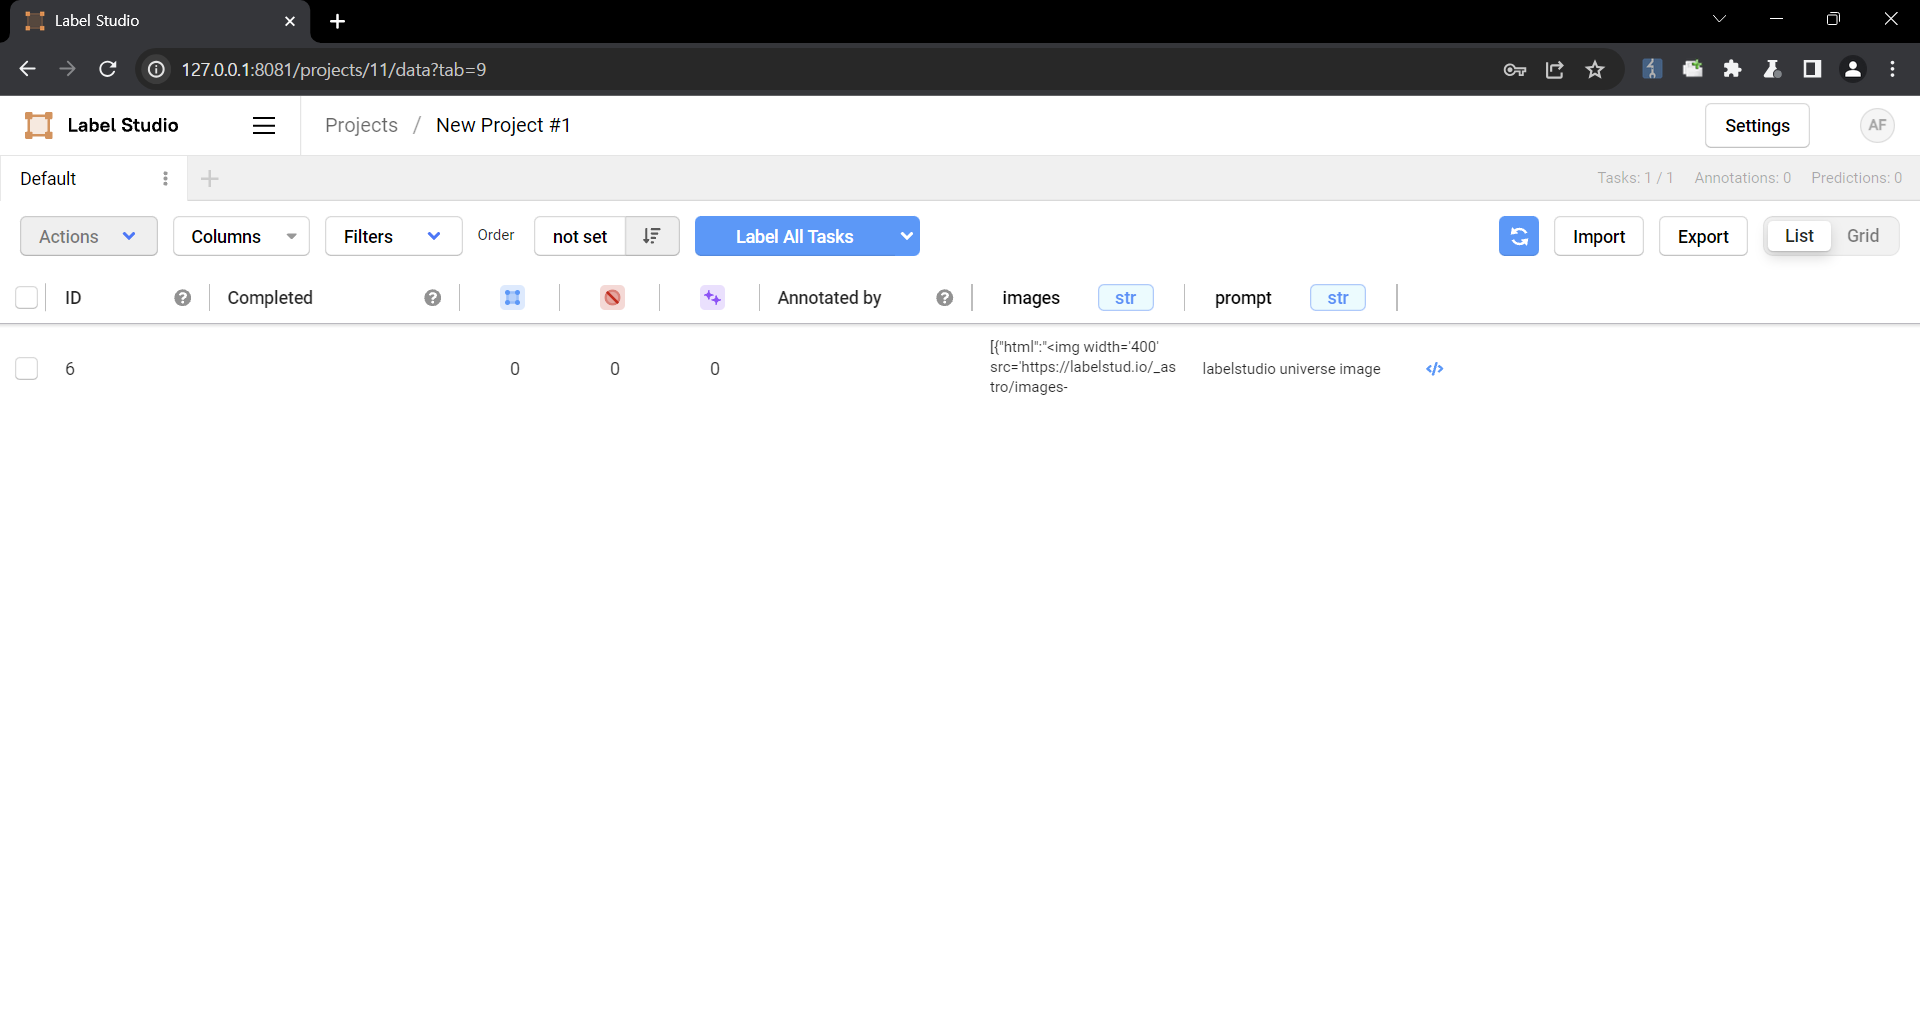 5. Check that the script is running 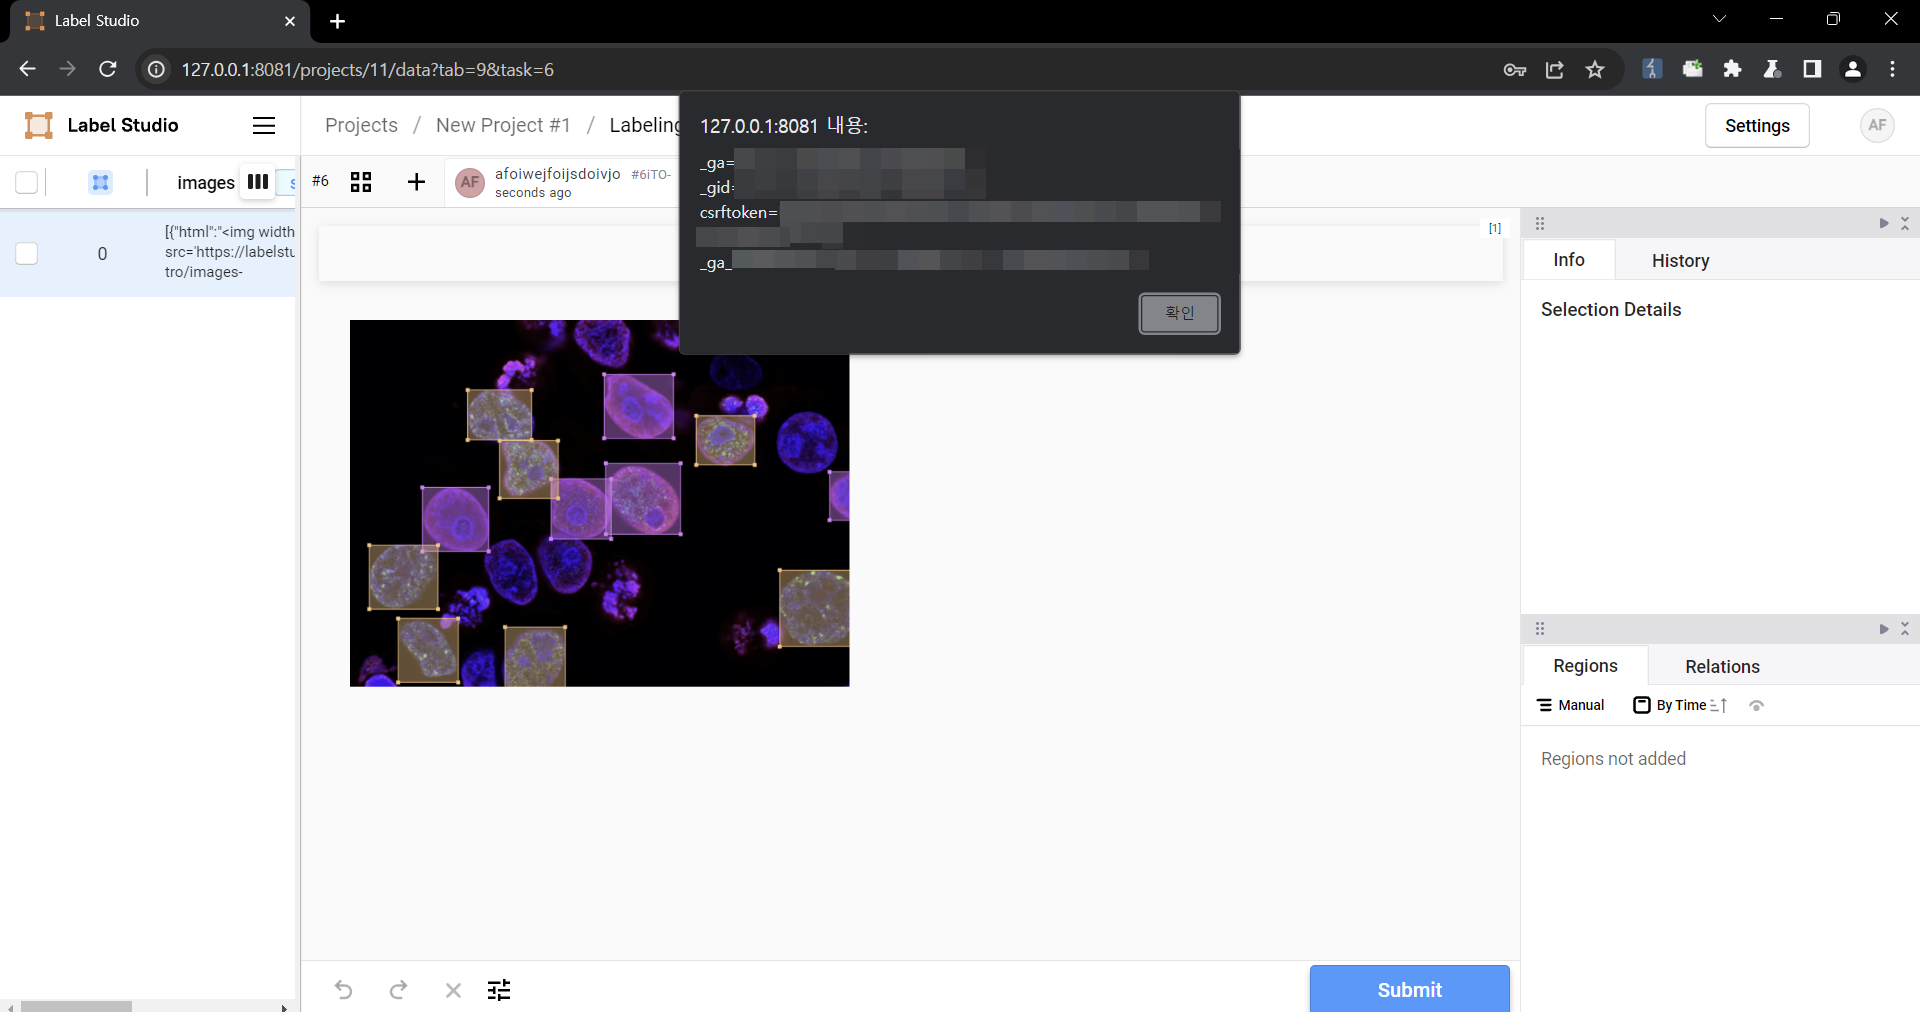 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
CVSS 4.7 · Mittel · EPSS 2,2% · Korrektur verfügbar
- Veröffentlicht
- Aktualisiert
Technologie-Stack: python
Betroffene Produkte und Versionen
label-studio
- Softwareversionen
- < 1.11.0: Betroffen
Keine Korrektur veröffentlicht
label-studio PyPI
- Softwareversionen
- 0.4.1
- 0.4.2
- 0.4.3
- 0.4.4
- 0.4.4.post1
- 0.4.4.post2
- 0.4.5
- 0.4.6
- 0.4.6.post1
- 0.4.6.post2
- 0.4.7
- 0.4.8
- 0.5.0
- 0.5.1
- 0.6.0
- 0.6.1
- 0.7.0
- 0.7.1
- 0.7.2
- 0.7.3
- 0.7.4
- 0.7.4.post0
- 0.7.4.post1
- 0.7.5.post1
- 0.7.5.post2
- 0.8.0
- 0.8.0.post0
- 0.8.1
- 0.8.1.post0
- 0.8.2
- 0.8.2.post0
- 0.9.0
- 0.9.0.post2
- 0.9.0.post3
- 0.9.0.post4
- 0.9.0.post5
- 0.9.1
- 0.9.1.post0
- 0.9.1.post1
- 0.9.1.post2
- 1.0.0
- 1.0.0.post0
- 1.0.0.post1
- 1.0.0.post2
- 1.0.0.post3
- 1.0.1
- 1.0.2
- 1.0.2.post0
- 1.1.0
- 1.1.0rc0
- 1.1.1
- 1.10.0
- 1.10.0.post0
- 1.10.1
- 1.2
- 1.3
- 1.3.post0
- 1.3.post1
- 1.4
- 1.4.1
- 1.4.1.post0
- 1.4.1.post1
- 1.5.0
- 1.5.0.post0
- 1.6.0
- 1.7.0
- 1.7.1
- 1.7.2
- 1.7.3
- 1.8.0
- 1.8.1
- 1.8.2
- 1.8.2.post0
- 1.8.2.post1
- 1.9.0
- 1.9.1
- 1.9.1.post0
- 1.9.2
- 1.9.2.post0
- Betroffene Versionsbereiche
- ECOSYSTEM: < 1.11.0
Auf 1.11.0 aktualisieren
label-studio PyPI
- Softwareversionen
- 0.4.1
- 0.4.2
- 0.4.3
- 0.4.4
- 0.4.4.post1
- 0.4.4.post2
- 0.4.5
- 0.4.6
- 0.4.6.post1
- 0.4.6.post2
- 0.4.7
- 0.4.8
- 0.5.0
- 0.5.1
- 0.6.0
- 0.6.1
- 0.7.0
- 0.7.1
- 0.7.2
- 0.7.3
- 0.7.4
- 0.7.4.post0
- 0.7.4.post1
- 0.7.5.post1
- 0.7.5.post2
- 0.8.0
- 0.8.0.post0
- 0.8.1
- 0.8.1.post0
- 0.8.2
- 0.8.2.post0
- 0.9.0
- 0.9.0.post2
- 0.9.0.post3
- 0.9.0.post4
- 0.9.0.post5
- 0.9.1
- 0.9.1.post0
- 0.9.1.post1
- 0.9.1.post2
- 1.0.0
- 1.0.0.post0
- 1.0.0.post1
- 1.0.0.post2
- 1.0.0.post3
- 1.0.1
- 1.0.2
- 1.0.2.post0
- 1.1.0
- 1.1.0rc0
- 1.1.1
- 1.10.0
- 1.10.0.post0
- 1.10.1
- 1.2
- 1.3
- 1.3.post0
- 1.3.post1
- 1.4
- 1.4.1
- 1.4.1.post0
- 1.4.1.post1
- 1.5.0
- 1.5.0.post0
- 1.6.0
- 1.7.0
- 1.7.1
- 1.7.2
- 1.7.3
- 1.8.0
- 1.8.1
- 1.8.2
- 1.8.2.post0
- 1.8.2.post1
- 1.9.0
- 1.9.1
- 1.9.1.post0
- 1.9.2
- 1.9.2.post0
- v1.4.1
- v1.4.0
- v1.3.0
- v1.2.0
- v1.1.1
- v1.1.0
- v1.0.2
- v1.0.1
- v1.0.0
- v0.9.1.post1
- v0.9.1.post0
- v0.9.0.post5
- v0.9.0.post4
- v0.9.0.post3
- v0.9.0
- v0.8.2
- v0.8.1
- v0.8.0
- v0.7.5.post0
- v0.7.3
- v0.7.2
- v0.7.1
- v0.7.0
- v0.6.1
- v0.6.0
- v0.5.1
- v0.4.8
- v0.4.7
- v0.4.6
- v0.4.5
- v0.4.4
- v0.4.0
- v0.3.0
- v0.2.2
- v.0.2.1-8
- v.0.2.1-5
- v.0.2.1-4
- v.0.2.1-3
- v.0.2.1-2
- v.0.2.0
- v.0.1.6
- v.0.1.5
- v.0.1.4
- v.0.1.2
- v.0.1.1
- v.0.1.0
- Betroffene Versionsbereiche
- GIT: < 5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- ECOSYSTEM: < 1.11.0
Auf 1.11.0 aktualisieren
Originalquellen
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg
- https://github.com/HumanSignal/label-studio/pull/5232
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0
- https://nvd.nist.gov/vuln/detail/CVE-2024-26152